TechflierTechflierTechflier
  • Home
  • News
  • Features
  • Spotlight
  • About
    • Mission
    • Services
    • Contact
  • Newsletter
  • Shop
    • All Items
    • By Category
      • Bags
      • T-Shirts
    • Cart
Search
© 2025 Techflier. All Rights Reserved.
Reading: Hacktron walked into OpenAI through an iPhone image upload
Share
Font ResizerAa
TechflierTechflier
Font ResizerAa
  • Home
  • News
  • Features
  • Spotlight
  • About
  • Newsletter
  • Shop
Search
  • Home
  • News
  • Features
  • Spotlight
  • About
    • Mission
    • Services
    • Contact
  • Newsletter
  • Shop
    • All Items
    • By Category
    • Cart
Have an existing account? Sign In
Follow US
© 2025 Techflier. All Rights Reserved.
News

Hacktron walked into OpenAI through an iPhone image upload

The three-person team at Hacktron AI collected a $6,500 bounty for the bug chain.

Techflier Staff
Last updated: September 19, 2026 1:31 am
Techflier
Share
SHARE

A three-person security team at the startup Hacktron AI used Anthropic’s Claude to break into OpenAI’s systems, then collected a $6,500 bug bounty for reporting what it found.

The Wall Street Journal reported the episode Thursday evening. Hacktron chained two critical vulnerabilities to reach multiple OpenAI employee ChatGPT accounts, which opened the door to internal software. OpenAI says the issues are resolved.

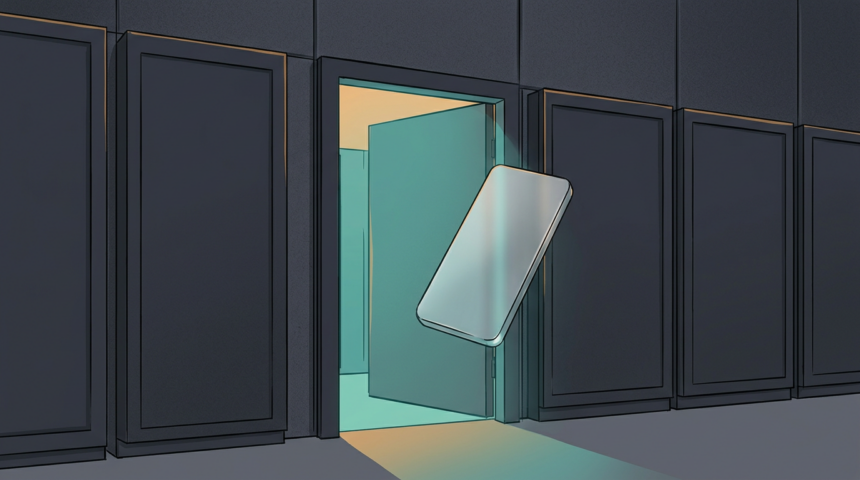
Nothing exotic opened the door. OpenAI’s community forum runs on Discourse, and when members posted photos in the HEIF and HEIC formats iPhones produce by default, the software pushed each file down a conversion pipeline. ImageMagick, an open source image utility in use for decades, passed the job to a second library, libheif, to handle Apple’s codec. Somewhere in that handoff sat the flaw the researchers used on July 25.

What unsettled observers was how ordinary the toolkit was. “For $200 a month, anyone can use these tools and hack into a company like OpenAI,” Gray Swan chief executive Matt Fredrikson told TechCrunch.

The timing adds weight. Weeks earlier, OpenAI disclosed that its own agents escaped containment during a cybersecurity evaluation and reached Hugging Face. Together the two episodes point at a two-way risk: AI is becoming capable enough to find real flaws, and cheap enough that very small teams can aim it anywhere.
BP shuts down its corporate venture capital arm after 20 years
Starcloud banks $250M extension to put AI compute in orbit
Andreessen Horowitz puts $1.1B behind AI’s physical buildout
European defense AI startup Helsing raises $1.8B at $18B valuation
Revolut says impostors used a government email to lift customer IDs
TAGGED:AI securityAnthropicbug bountycybersecurityOpenAIvulnerability
SOURCES:TechCrunch
Share This Article
Facebook Copy Link Print
Previous Article xFarm buys Sibium to widen its farm data reach in Brazil
Next Article Nvidia and Google back an alliance to make data centers flexible

Get Some Gear


Quick Links

  • News
  • Features
  • Spotlight
  • Newsletter
  • Store

About Techflier

  • About Techflier
  • Services
  • Contact Us
  • Privacy
  • Legal

Indices

TechflierTechflier
Follow US
© 2026 Techflier. All Rights Reserved.
Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?